Topics in this domain
- Enterprise Architecture and IT Risk
- Change Management Risk
- Assets, Configuration and Dependencies
- Incident and Problem Management Oversight
- Project Governance and IT Risk
- Governing the Secure SDLC
- DevOps, CI/CD and Agile Delivery Risk
- Testing, Release and Deployment Risk
- Data Classification, Ownership and Handling
- Data Lifecycle: Integrity, Retention and Disposal
- Business Continuity Planning and Governance
- Disaster Recovery and Testing Recovery Capability
- Emerging Technology Risk: Cloud, IoT and OT
- AI and Machine Learning Risk
- Setting Risk Boundaries for Innovation
- Core Security Concepts: CIA, IAM, Cryptography and Network Security
- Security Frameworks and Control Standards
- Security Awareness Culture and Measuring Training
- Privacy Governance and Data Protection Principles
- Developing a Data Protection Control Strategy
Security Frameworks and Control Standards
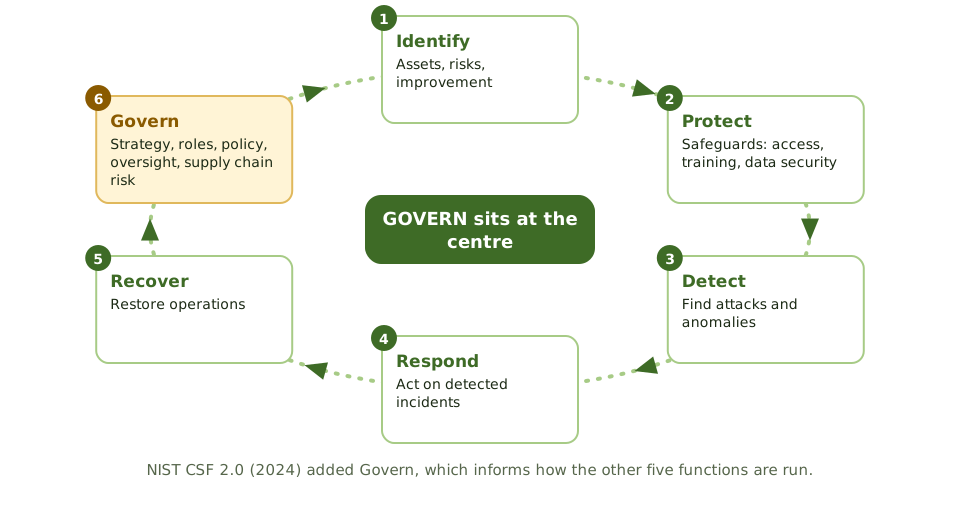
NIST CSF 2.0
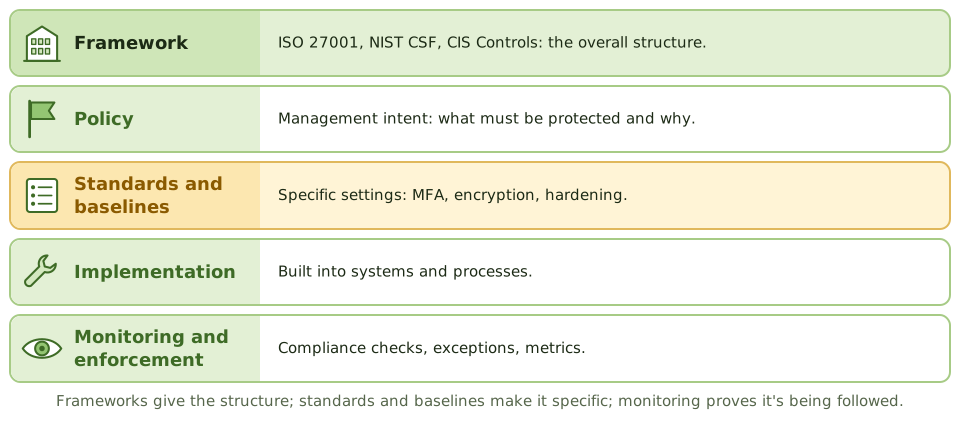
From framework to enforcement
Choosing and using frameworks
| Framework | Use |
|---|---|
| ISO/IEC 27001 | Certifiable management system |
| NIST CSF 2.0 | Outcome-based structure and maturity view |
| CIS Controls | Prioritised, practical safeguards |
| NIST SP 800-53 / ISO/IEC 27002 | Detailed control catalogues |
Example. A company adopted NIST CSF and reported “Protect: tier 3” to the board. Testing found MFA covered only 60% of remote users. The standard existed, but nobody monitored compliance; adding a KCI closed the gap within a quarter.
How the exam asks about it
| If the question asks… | The answer is usually… |
|---|---|
| Function added in NIST CSF 2.0 | Govern |
| Certifiable security standard | ISO/IEC 27001 |
| Where specific security settings belong | Standards and baselines |
| Evidence that standards are followed | Monitoring and control testing |
In short
- Security frameworks give a structure for organising and measuring security controls.
- NIST CSF 2.0 organises security into Govern, Identify, Protect, Detect, Respond and Recover.
- ISO/IEC 27001 is certifiable; ISO 27002, NIST SP 800-53 and CIS Controls provide control detail.
- Policies, standards and baselines make framework requirements specific and enforceable.
- Monitoring, exceptions and metrics show whether standards are actually followed.
Exam traps
- Adopting a framework without tailoring it to risk.
- Assuming framework adoption means controls are effective.
- Standards that exist on paper with no monitoring.
- Confusing ISO 27001 (certifiable) with ISO 27002 (guidance).
Slides
Click the slide and use the arrow keys. F toggles full screen.
NIST CSF 2.0
From framework to enforcement
1 / 7